# Authentication ## Which User is it? --- #### Core Problem Which user is currently using the device? Challenge: The "user" can't do anything a computer can do -- But they can LIE --- **Authentication**: Which user is in front of the keyboard? **Authorization**: What is that user allowed to do? --- #### How to do Authentication * Ask the user to do something * Must be something only *that* user can do * Must be something easy for computer to verify * Can't be something that is easy for computers to fake * Can't be something that is easy for other people to fake * Can't be something that is easy to emulate / steal? Note: Write these on whiteboard --- #### Extra Challenges * Must be easy, since they will do it A LOT * Must be different for different systems / websites * Must be able to be changed (in case of compromise) * Should be *tunable* -- make it harder or easier as needed * As it gets harder, it should get disproportionally more difficult for attackers than defenders Note: Write these on whiteboard --- Factors of Authentication * Something you know (password) * Something you have (2nd device) * Something you are (biometric) * Someone you know (friend auth) --- # Examples of Authentication Schemes Note: For each of these, how well do they satisfy auth goals? * Must be something only *that* user can do * Must be something easy for computer to verify * Can't be something that is easy for computers to fake * Can't be something that is easy for other people to fake * Con't be something that is easy to emulate / steal? * Must be easy, since they will do it A LOT * Must be different for different systems / websites * Must be able to be changed (in case of compromise) --- ## Something you know --- ### Password Login 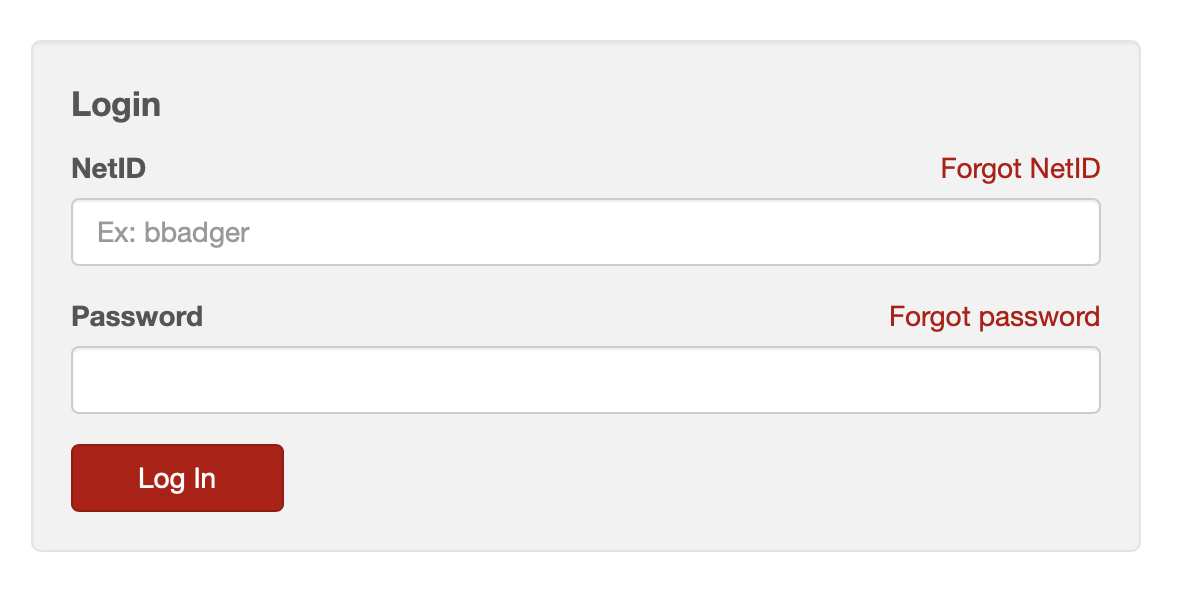 --- ### Pattern Swipe 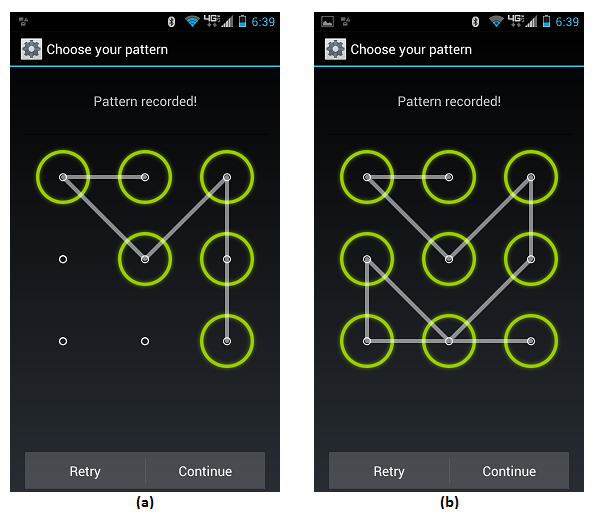<!-- .element height="500" --> (Subject to [Smudge Attacks](https://www.usenix.org/legacy/event/woot10/tech/full_papers/Aviv.pdf)) --- ### Pass Points (click-based passwords) 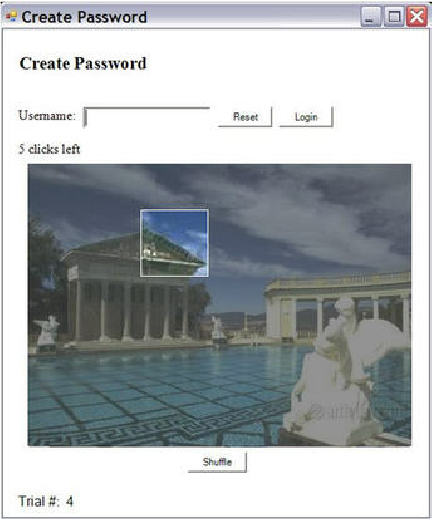 --- ### Pass Faces 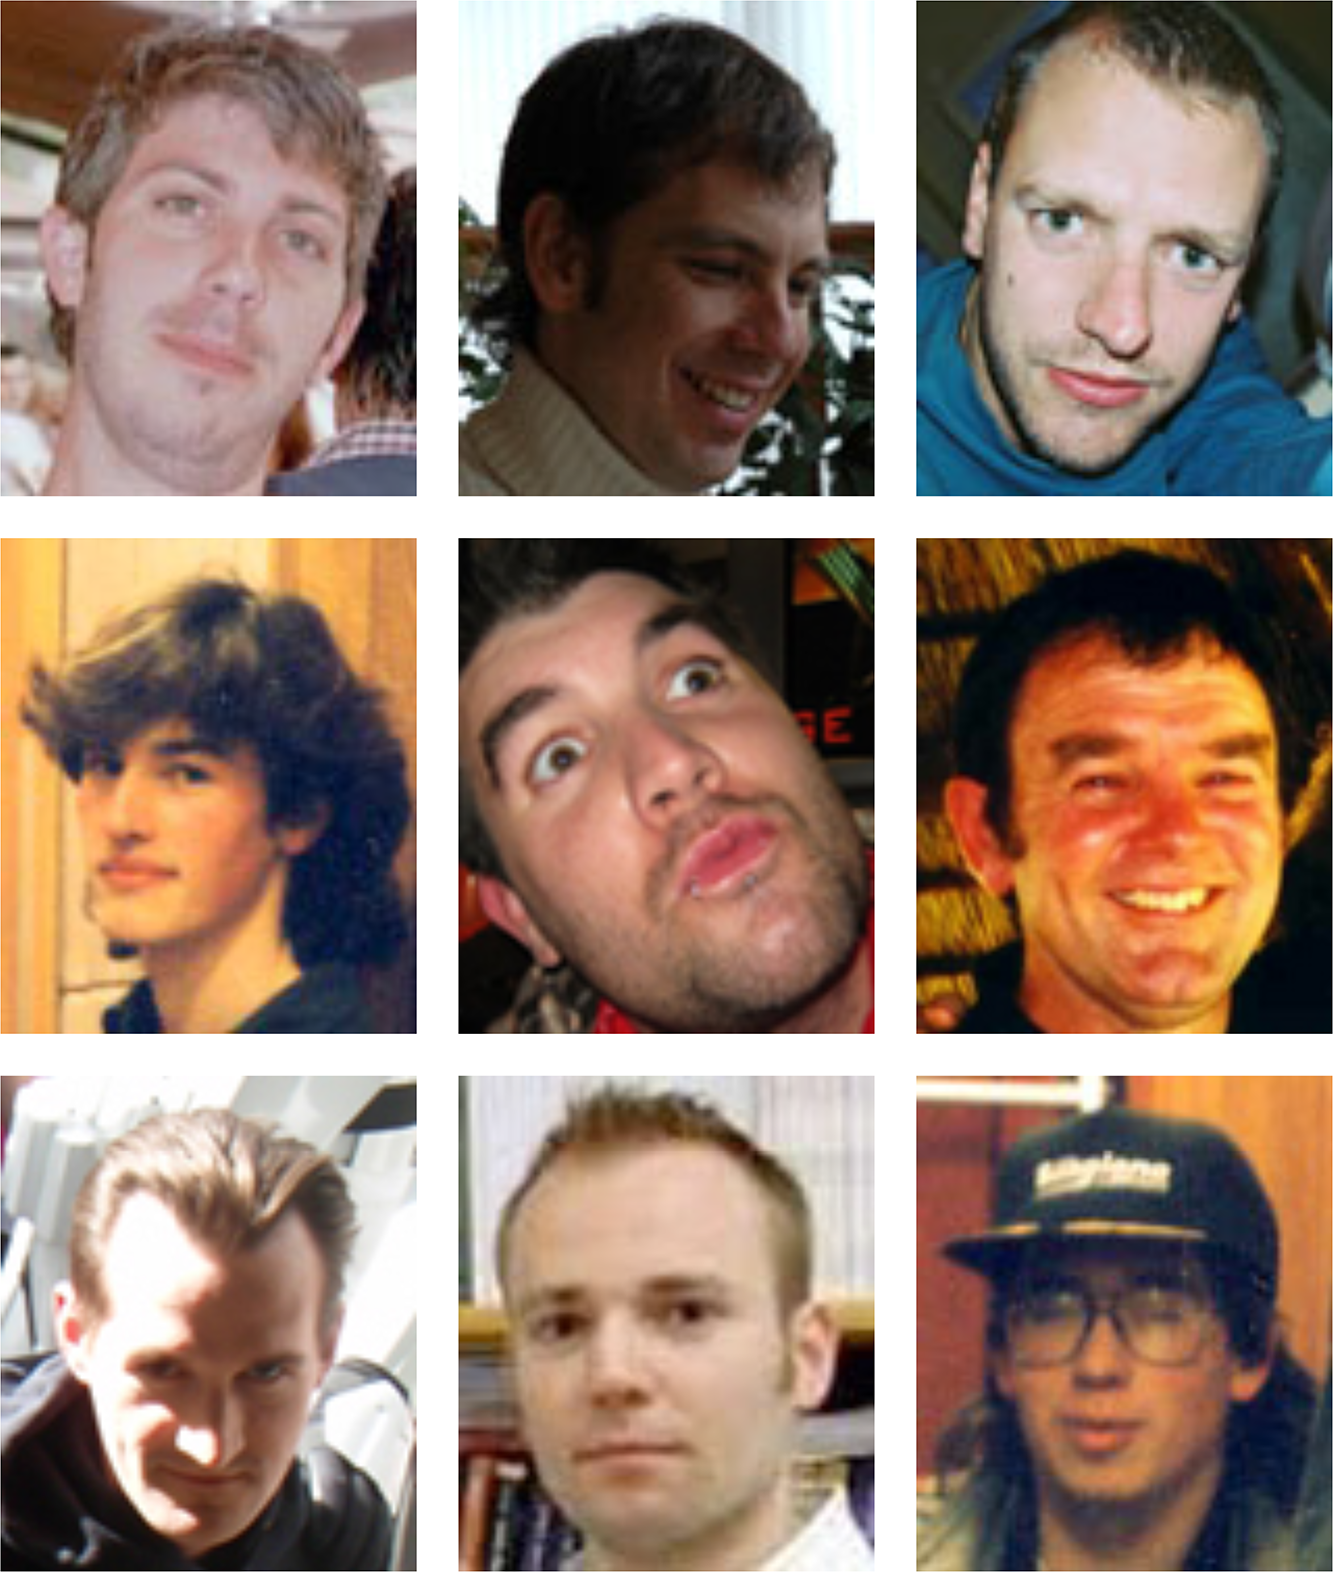<!-- .element height="500" --> --- ## Something You Have --- ### RSA SecureID  --- ### Yubikey 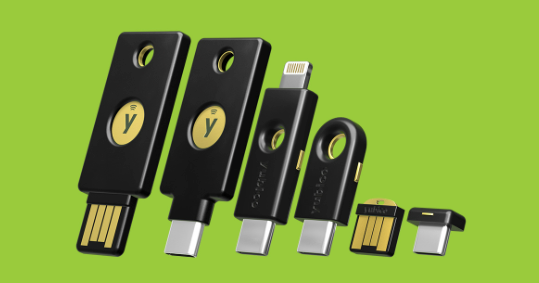<!-- .element height="500" --> --- ### One-time Passwords 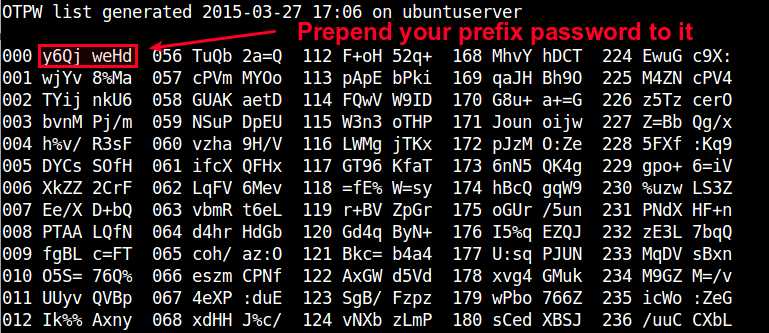 --- ### Time-Based One-time Passwords (TOTP) 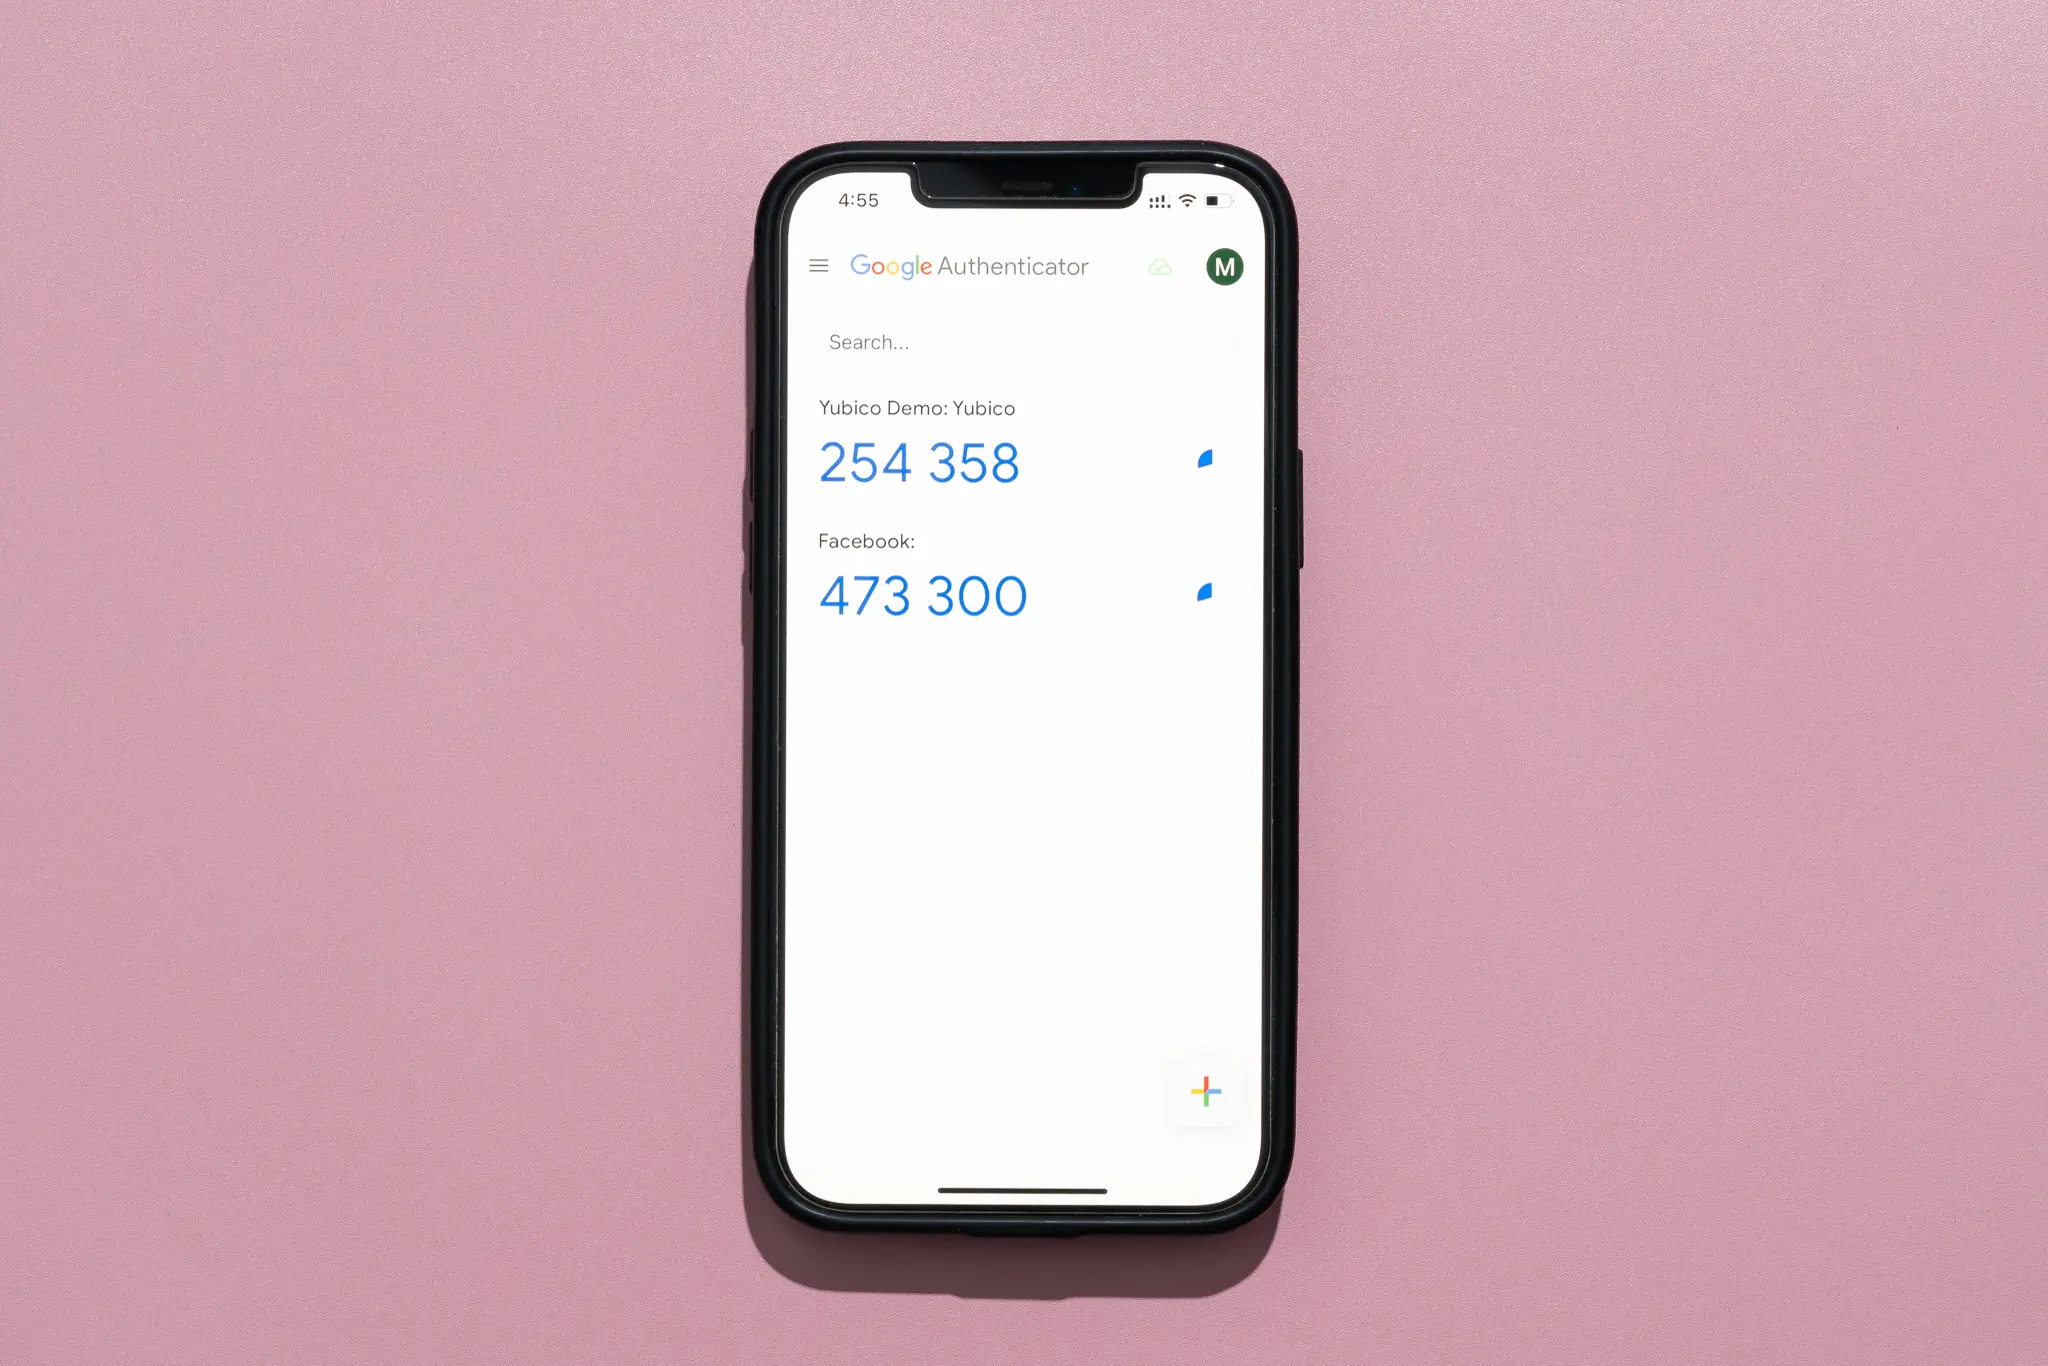<!-- .element height="500" --> --- ### Pico 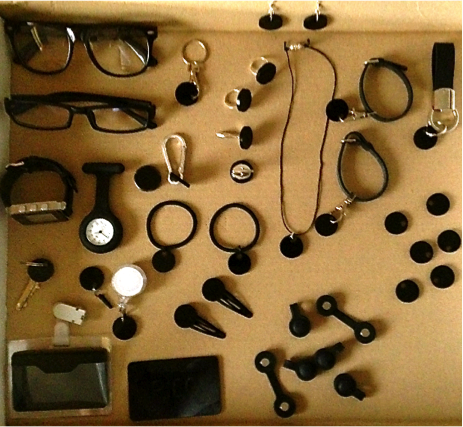<!-- .element height="500" --> --- ## Something You Are --- ### Fingerprint Reader <!-- .element height="500" --> --- ### Face ID 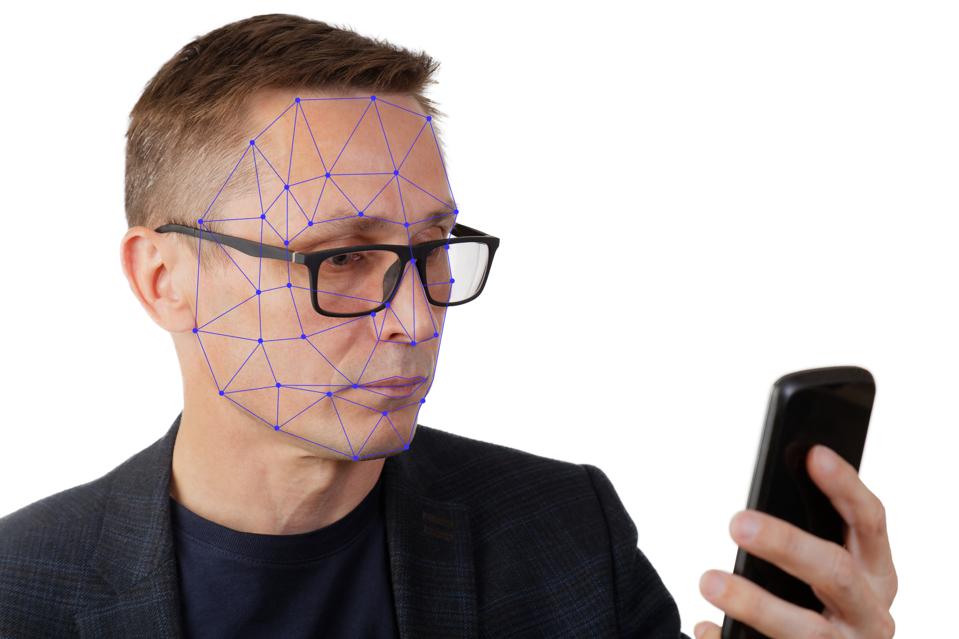 --- ### Continuous Authentication <!-- .element height="500" --> --- ### Walking Gait <!-- .element height="500" --> --- ## Someone you Know --- ### Facebook Social Verification 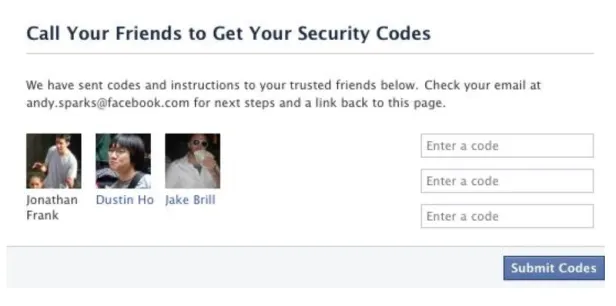 --- ## Multi-Factor Authentication Do more than one of those