# Passwords --- ## Passwords have a "Life Cycle" --- 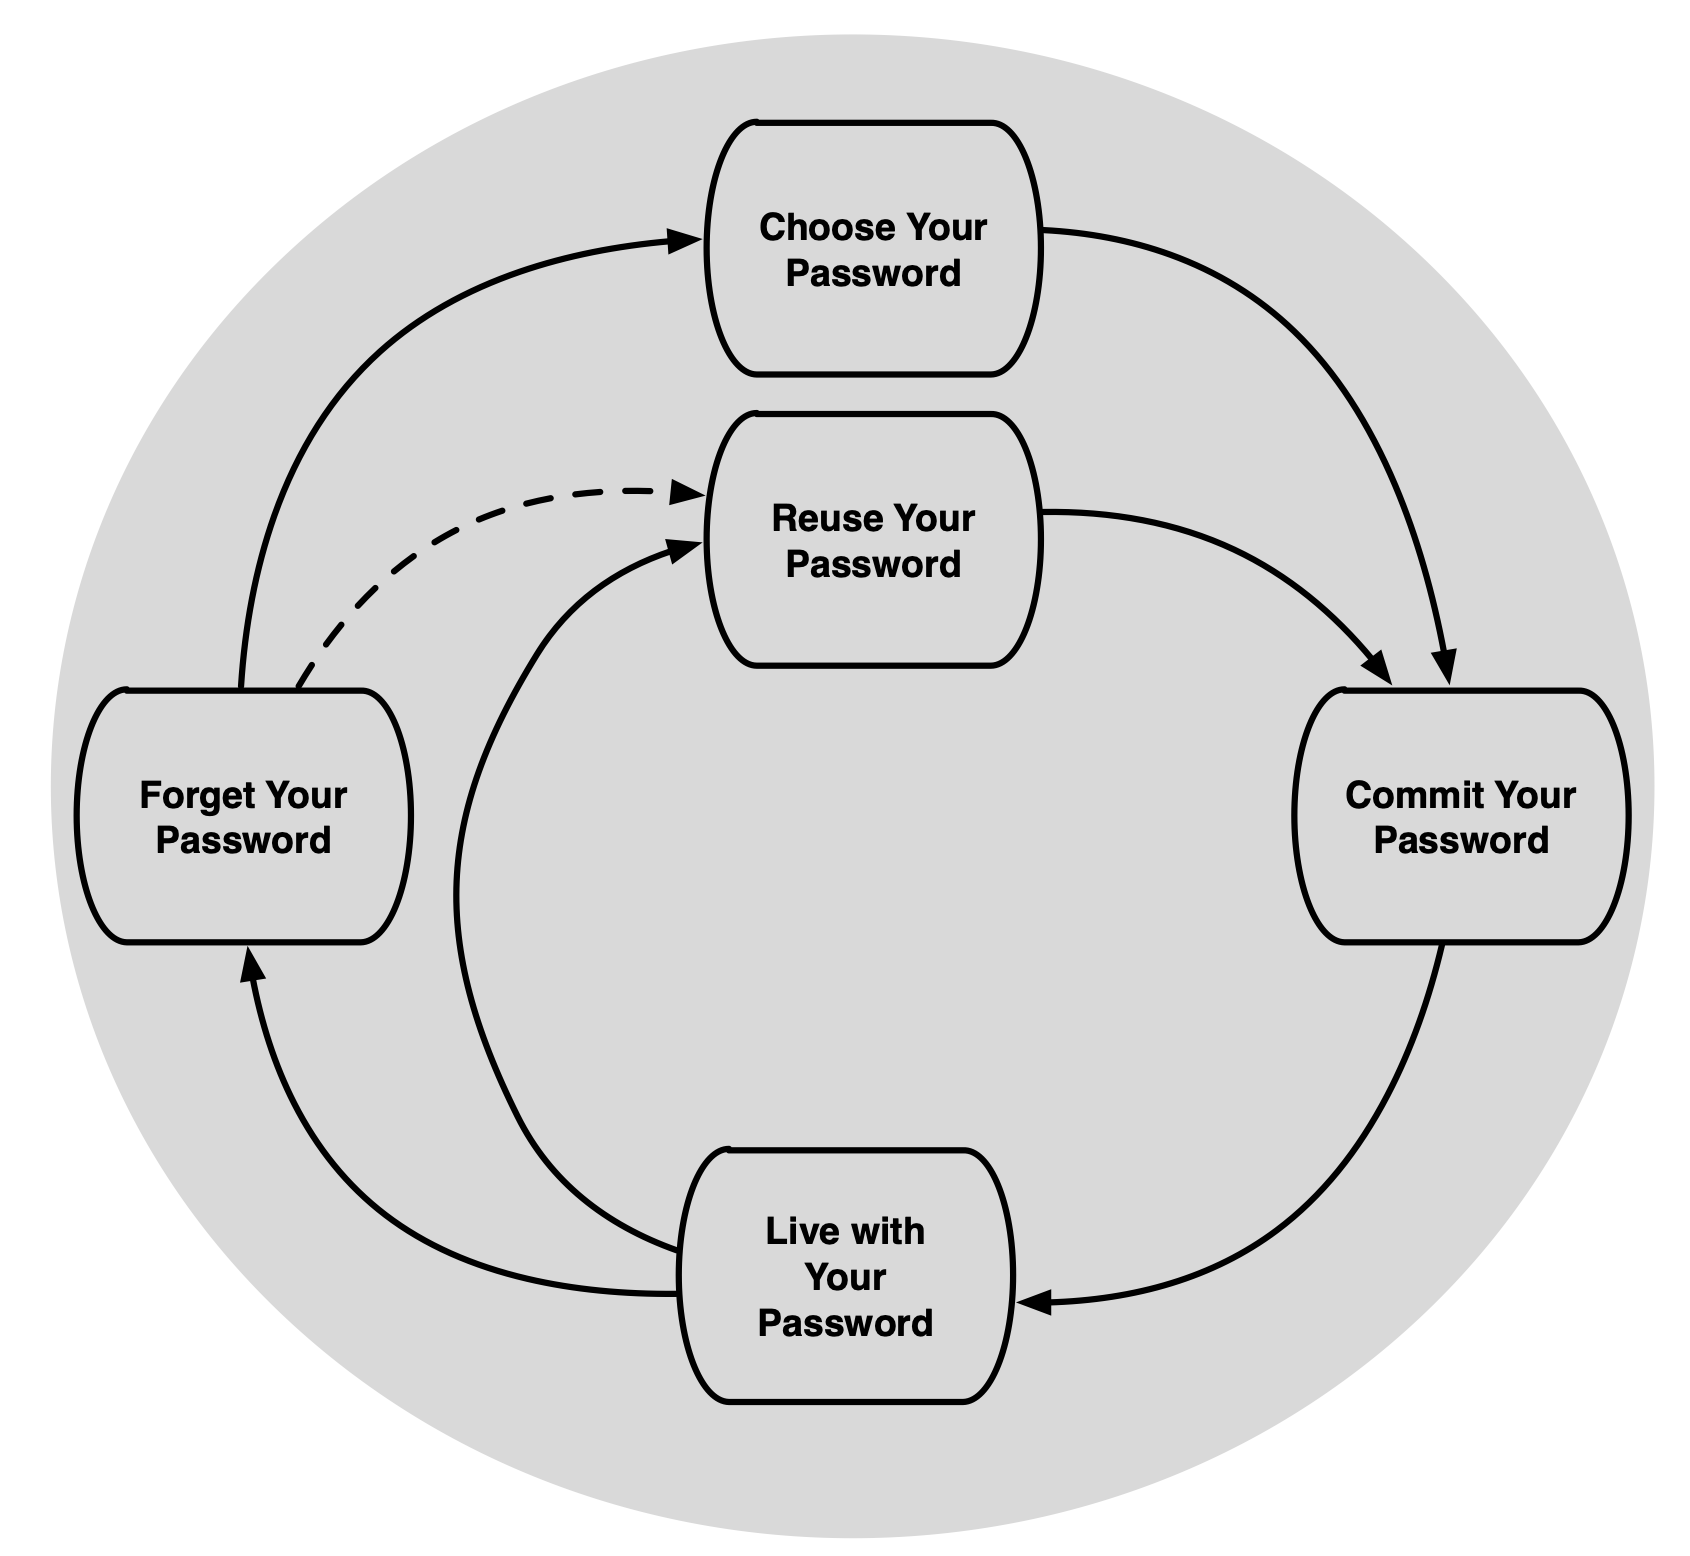 <!-- .element height="650" --> Note: Choose your Password / Reuse your Password Commit your Password Live with your Password Forget your Password --- ## Password threat models Who is the adversary? Note: Targetted personal attacks Anonymous large-scale password hacks Loss of private data --- ## Modern Password Usability Challenges * Password rules / requirements * Password reuse (same system) * Password reuse (across systems) * Password expiration Note: Spaces? --- <!-- .slide: data-auto-animate --> ## Password Rules * Must be at least 15 characters * Must include at least 3 different types of characters * Must not be the same as last 5 passwords you used * Must ... --- <!-- .slide: data-auto-animate --> ## Password Rules Are rules positive or negative for security? What threat do the rules address? --- ## Password reuse * Most people have 4-8 passwords (total) * And variations * Most-reused password is used on about 10 websites * People tend to reuse more complex passwords * Incorrect passwords are frequently passwords to other websites --- <!-- .slide: data-auto-animate --> ## Password Expiration How often should you change your password? --- ## Password Expiration <!-- .slide: data-auto-animate --> * NIST (In past): every 90 days * NIST (now): Only when compromised --- <!-- .slide: data-auto-animate --> ## Password Managers Two types: * Just saves passwords (Chrome, safari built-in) * Also *generates* passwords (1Password, LastPass) --- <!-- .slide: data-auto-animate --> ## Password Managers Two motivations * Convenience: make things easier * Security: generate (rather than memorize) strong passwords